
Know exactly what's exposed. Patch what matters first.
Version-precise OT/ICS vulnerability intelligence, matched to the exact firmware on your equipment. Delivered as a managed service, by API, or straight to your AI agent over MCP.
Connect your agent to version-precise OT vulnerability data.
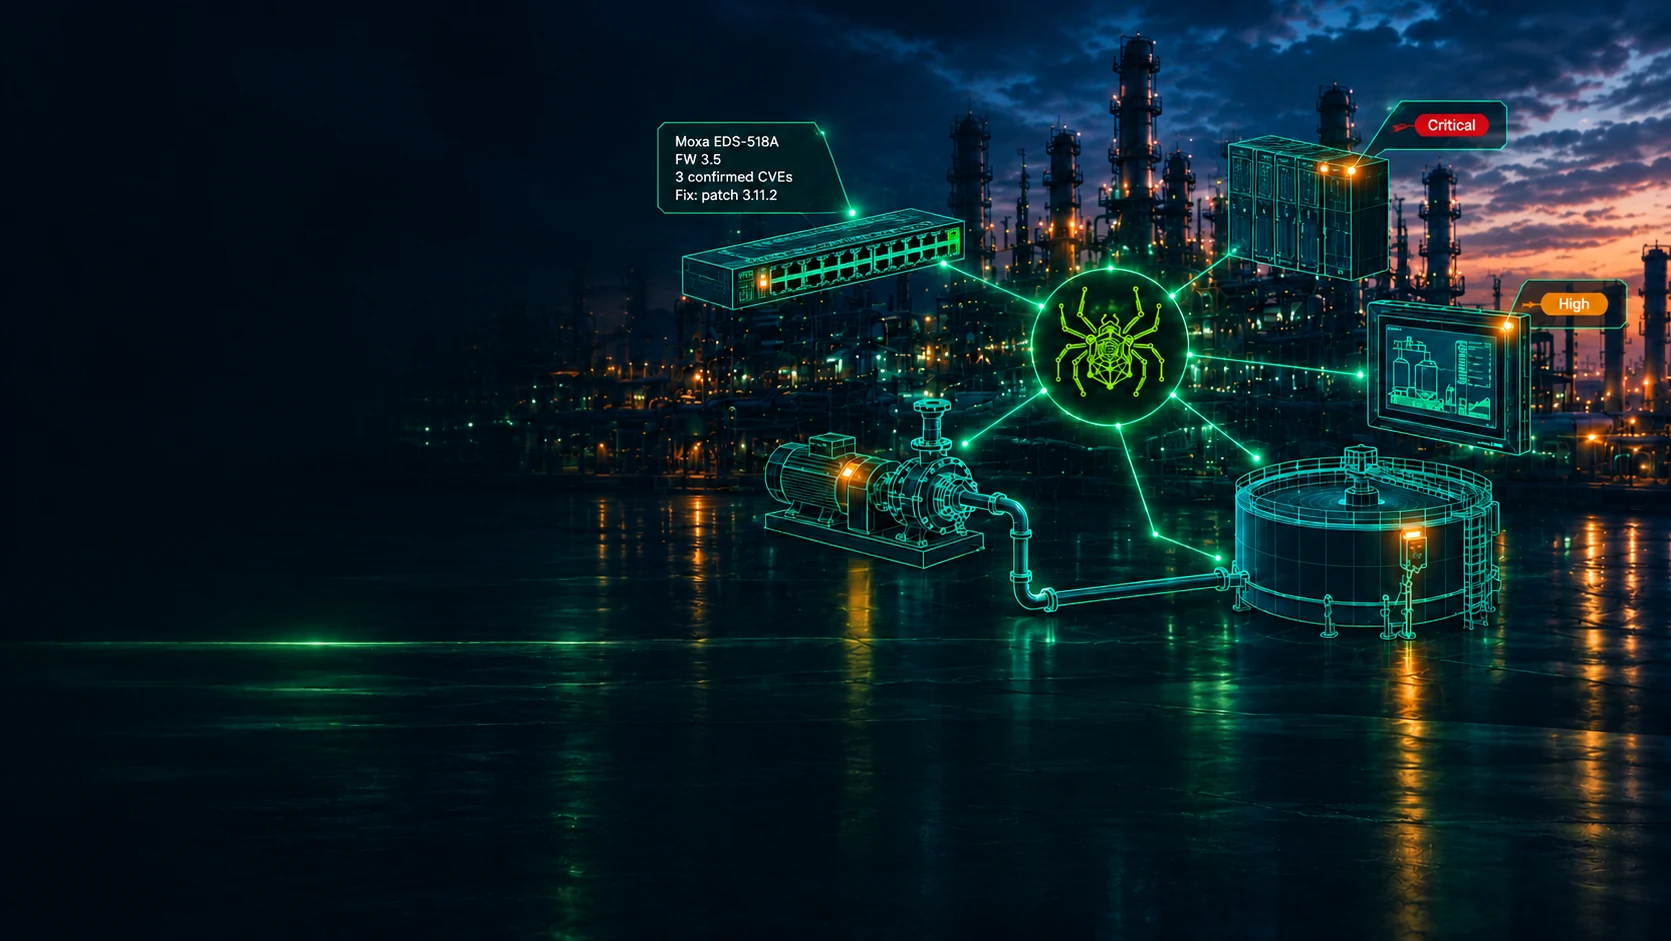
Send a device's vendor, product and firmware. Get back only the vulnerabilities that apply to that exact version, with the source behind each one, a fix-first rank and the action that clears it.
Works with any MCP-compatible agent through the BreachSpider MCP package.
POST /api/v1/assets/correlate-cves
{"assets": [{"asset_id": "SWITCH-01", "vendor": "Moxa",
             "product": "EDS-518A", "version": "V3.5"}]}
"cves_page": {"total": 3},
"cves": [{
  "cve_id": "CVE-2024-9137",
  "match_tier": "RANGE",
  "affected_range": {"version_start": "1.0", "version_end": "3.11"},
  "priority_rank": 1,
  "fix": {
    "action": "upgrade to security patch 3.11.2 (from Moxa Technical Support)",
    "derived": false,
    "document": "MPSA-241156"
  }
}, ...]
Built for agents that can't afford to guess
An agent is only as good as the data it pulls. BreachSpider is designed so an agent can't misread it.
Evidence on every finding.
Each match carries the affected version range and the source it came from, so the agent cites instead of guessing.
Confidence is explicit.
Each finding is marked as confirmed for the installed version, a product-level match, or needing review.
Empty never means clean.
When coverage is partial or missing, the result says so. An agent can't report a device as safe just because nothing matched.
Fix-first order, with a reason.
Results are ranked in the order to act, each with a plain-language reason the agent can pass straight to a person.
One action per group.
Findings are grouped under the single update or firmware upgrade that clears them.
Check, don't resubmit.
Each device result carries a hash. A lightweight check call tells the agent whether anything changed, so it only acts when something new applies.
The agent finds and ranks. A person decides.
Connect in minutes
Get an API key.
Keys are tied to your organization, with read and write scopes.
Load the spec or the SDK.
Point your agent framework at the OpenAPI 3.1 specification, or use the open Python SDK with typed models, automatic paging and retries that respect rate limits.
Make the call.
Plain HTTP works from any language, including scripts with no installs.
Windows hosts, decided per CVE
Engineering workstations, historians and HMI servers usually hold the most vulnerabilities. Send the OS build and installed updates, and BreachSpider decides every Microsoft CVE for that host: confirmed open, already patched, or needs review. Each decision comes with the fixed build, the KB to install and the Microsoft source it rests on. When evidence conflicts, the result says needs review. It never guesses.
The Windows API refuses identifying data such as hostnames, IP addresses and user names, so an agent can't send them by accident.
Three ways to use BreachSpider
Managed monitoring
We monitor your assets continuously and alert you when something new applies. Recurring reporting is included.
API
Your agent, platform or team calls BreachSpider directly and builds the results into your own tools.
OEM
Build BreachSpider intelligence into your own product, for every customer you serve.
Need full separation? Any customer can run on a dedicated node that serves only them, hosted in the region their data rules require.
How an engagement works
Assess.
Every engagement starts with an assessment of the sites, assets and versions in scope, delivered by our OT assessment partner.
Onboard.
Your inventory is checked for completeness, and identifying information is removed before it enters BreachSpider.
Monitor.
Findings for your exact versions, watched as new vulnerabilities are published.
Report.
Framework-aligned reporting that supports NERC CIP and IEC 62443 work.
Checked against the source
Independent Windows check.
On 15 test hosts, BreachSpider matched a separate checker that reads Microsoft's raw data with its own code, with no differences across more than 40,000 per-CVE decisions.
Real-site comparison.
On a real industrial site's asset export, every difference with a leading commercial OT platform was checked against the vendors' own advisories.
Isolated by default.
Every customer is separated at the database level, and the device API stores no submitted asset data.
Scoped to your project.
Every engagement is scoped to what you actually run and how you want it delivered: API, managed monitoring or OEM. You receive a written scope and a fixed quote before anything begins.
Search any CVE, free.
Create a free account to search BreachSpider's CVE database, with version ranges and sources on every entry.